Slothoku199jp.live Review: Rogue Casino Architecture, Stealth PWA Payloads, and Financial Recovery Protocols

The illicit iGaming portal operating under the domain Slothoku199jp.live represents an active financial threat engineered by an offshore cybercrime syndicate. While presenting itself as an elite, high-roller online casino and sports-betting interface, forensic domain reconnaissance confirms that the property functions as an unlicensed, disposable front designed to siphon consumer capital across Tier-1 jurisdictions, specifically targeting players and diaspora communities in the United States, the United Kingdom, Canada, and Australia. By deploying misleading localized branding alongside browser-level exploits, the operators isolate victims within an unregulated digital environment devoid of consumer protections, statutory oversight, or genuine payout liquidity.
1. Domain Forensics & Churn Architecture
The structural composition of Slothoku199jp.live is characteristic of automated, programmatic domain churn networks. The URL taxonomy adheres to an industrialized operational template:
- Brand Identifier:
Slothoku(mimicking regional lottery and Japanese-themed pachislot brands to engineer false familiarity) - Sequential Seed:
199(an automated numerical iterator indicating advanced sequence progression in an expansive mirror farm) - Geographic Tag:
jp(synthetic regional targeting designed to misdirect compliance filters and local network blocks) - Disposable Top-Level Domain (TLD):
.live(a low-cost, low-reputation generic TLD acquired in bulk through privacy-shielded offshore registrar accounts)
[ Brand Seed: "Slothoku" ] + [ Sequential Iterator: "199" ] + [ Geo Tag: "jp" ] . [ High-Churn gTLD: "live" ]
To evade automated blacklists, web-filtering engines, and proactive threat intelligence platforms, the operators deploy aggressive DNS CNAME aliasing and reverse proxy mitigation layers. Any edge-node probe resolves back to ephemeral Content Delivery Network (CDN) proxies that obscure the true upstream IP addresses hosted within bulletproof data centers in non-cooperative offshore jurisdictions.
The domain utilizes short-TTL (Time-To-Live) DNS round-robin routing. When telecommunications regulators, law enforcement, or national gaming boards blacklist Slothoku199jp.live, a cluster management script updates the DNS records to route inbound web traffic to alternate iterations within seconds. This operational agility is cataloged extensively in our investigation into disposable mirror infrastructures and reverse-proxy syndicates, which details how modern syndicates sustain uninterrupted victim acquisition despite regulatory sanctions.
2. Technical Threat Vector: Progressive Web App (PWA) Stealth Payloads
The primary threat vector deployed by Slothoku199jp.live relies on Progressive Web App (PWA) stealth payloads paired with background service worker manipulation. Rather than funneling victims into native app stores—where mandatory security scans, app-signing verifications, and compliance checks by Google or Apple would flag the platform immediately—the platform tricks the user into installing an out-of-store web application.
Victim Visits Slothoku199jp.live Mobile / Desktop Viewport
                           │
                           ▼
High-Urgency Prompt: "Install VIP App for 100% Unrestricted Access"
                           │
                           ▼
Browser Installs Manipulated Web App Manifest (manifest.json)
                           │
                           ▼
Browser Chrome Stripped (Padlock, Address Bar, & Cert Flags Hidden)
                           │
                           ▼
Persistent background service-worker.js Injected into Local Browser Engine
                           │
                           ▼
Continuous DOM Request Interception & Automated Credential Exfiltration
- Manipulated Web App Manifest (
manifest.json): Upon visiting the site via a mobile or desktop browser, aggressive pop-up overlays prompt the user to “Add to Home Screen” or “Download the VIP App for 100% Secure Access.” Accepting this downloads a tailored Web App Manifest that strips away native browser controls, address bars, and cryptographic security badges (such as SSL padlock indicators), running the interface in full-screen standalone mode. - Service Worker Injection & Cache Trapping: Once authorized, the site registers a persistent background
service-worker.js. This worker intercepts all network requests (fetchevents) between the client viewport and the origin server. - Client-Side DOM Manipulation & Dynamic Phishing: The service worker enables client-side DOM injection. If the user attempts to inspect network logs, exit the application, or view withdrawal disclosures, the service worker serves locally cached fallback assets, concealing runtime server errors and suppressing browser-level security warnings.
- Covert Telemetry & Credential Harvesting: Operating silently in the background via the Background Sync and Push APIs, the service worker captures unmasked authentication cookies, session tokens, and credit card autofill sequences entered into manipulated deposit inputs, beaming the exfiltrated payloads back to encrypted command-and-control (C2) micro-endpoints.
3. Financial Trap & Advance-Fee Fraud Mechanics
The deposit-to-withdrawal cycle on Slothoku199jp.live is entirely fabricated. The platform operates on a closed-loop, simulated liquidity framework designed to extract maximum capital through programmatic psychological manipulation.
Deposit Ingestion (Non-Reversible Rails)
           │
           ▼
Algorithmic Near-Miss & Synthetic Win Curve
           │
           ▼
Liquidity Blockade (Account Suspension / Pending Queue)
           │
           ▼
Advance-Fee Extortion Demands ("AML Tax Fees" / "VIP Verification Bonds")
           │
           ▼
Permanent Communication Blackout (Complete Capital Loss)
The underlying gaming engine does not connect to certified Random Number Generators (RNG) audited by independent testing houses like eCOGRA, BMM Testlabs, or iTech Labs. Instead, proprietary scripts manipulate slot volatility and return-to-player (RTP) curves client-side. Initial micro-wagers trigger artificial winning streaks, inflating the victim’s displayed account balance.
The trap snaps shut at the cashier portal:
- Payment Rail Segregation: The platform systematically rejects consumer-friendly clearing mechanisms (such as Visa/Mastercard zero-liability or domestic ACH networks) in favor of non-custodial and irreversible rails: Tether (USDT on TRC-20), unhosted Bitcoin wallets, Zelle, Interac e-Transfer, and Australian PayID transfers directed to third-party money mule rings.
- The Liquidity Blockade: When a user initiates a withdrawal, the system moves the request into a permanent “Manual Security Review” status.
- Advance-Fee Extortion: Support agents, operating via anonymous Telegram channels or live-chat widgets, inform the victim that their balance is frozen under international financial compliance laws. Release requires upfront out-of-pocket fees: an “Anti-Money Laundering (AML) Authentication Bond,” a “20% Capital Gains Escrow Fee,” or an “Expedited VIP Channel Clearance Deposit.” Paying these secondary assessments results in immediate account termination and a total communications blackout.
A forensic audit of the platform’s administrative footer reveals entirely fabricated licensing seals claiming authorization from the UK Gambling Commission (UKGC), the Malta Gaming Authority (MGA), the Kahnawake Gaming Commission, and state-level bodies like the Nevada Gaming Control Board. None of these statutory registries contain records for Slothoku199jp.live or its umbrella operating entities.
4. Legal Recourse, Banking Dispute Protocols & Asset Tracing
Victims of Slothoku199jp.live must treat the interaction as an intentional financial breach rather than a standard commercial disagreement. To maximize capital recovery and prevent secondary identity fraud, initiate the following forensic countermeasures immediately:
Fiat Banking & Card Network Disputes
- Card-Not-Present Chargebacks: If deposits were processed via debit or credit card through intermediary payment gateways, contact the issuing bank’s fraud investigations unit immediately. Request a formal credit card transaction dispute under Chargeback Reason Code 10.4 (Card-Absent Environment) for Visa or Reason Code 4837 (No Cardholder Authorization) for Mastercard. Emphasize that the merchant misrepresented digital gambling services using deceptive merchant category codes (MCC manipulation).
- Statutory Financial Protections: In the United States, assert rights under the Fair Credit Billing Act (FCBA) 15 U.S.C. § 1666 for credit card transactions, or invoke Regulation E (12 CFR Part 1005) for unauthorized electronic funds transfers involving debit cards and automated clearing houses. Consumers in the UK and Australia should invoke the Payment Services Regulations 2017 and the ePayments Code, respectively.
- Bank Wire Fraud Recall: If transfers were routed via bank wire, direct your financial institution to issue an emergency bank wire fraud recall using an ISO 20022 messaging / SWIFT MT199 message recall for fraudulent inducement to freeze destination intermediary accounts.
Crypto Forensics & Blockchain Asset Tracing
- Ledger Clustering: For deposits executed in USDT, BTC, or ETH, compile precise transaction hashes (TXIDs), destination public keys, and internal timestamp logs.
- Tracing & Allowance Revocation: Utilize blockchain analysis platforms to perform blockchain address clustering, mapping the movement of siphoned assets through unhosted wallet tracing into centralized exchange (CEX) deposit consolidation wallets. If a Web3 browser extension was connected directly to the domain, immediately execute a smart contract allowance revocation using automated authorization scanners (
revoke.cashor Etherscan Token Approval tool) to neutralize active smart contract drainers. - AML Compliance Ingestion: File an expedited AML compliance reporting dossier directly with the compliance departments of any centralized exchanges identified as host nodes for the destination consolidation wallets to freeze the illicit liquidation pipeline.
Regulatory Submissions
Formalize the incident with law enforcement and financial watchdogs to establish an official evidentiary paper trail:
- United States: File an internet crime report with the FBI Internet Crime Complaint Center (IC3), lodge a Federal Trade Commission (FTC) fraud submission via ReportFraud.ftc.gov, and submit a Consumer Financial Protection Bureau (CFPB) escalation against non-compliant payment clearing intermediaries.
- United Kingdom: Register a direct UK Action Fraud report with the National Fraud & Cyber Crime Reporting Centre and file an unlicensed gambling jurisdiction complaint with the UKGC intelligence division.
- Canada & Australia: Submit forensic logs to the Canadian Anti-Fraud Centre (CAFC) and the Australian National Anti-Scam Centre (Scamwatch).
5. Definitive Verdict & Risk Assessment
Slothoku199jp.live is an unverified, predatory digital gambling shell engineered to harvest consumer assets and sensitive banking data. Continued interaction poses severe financial and identity theft liabilities.
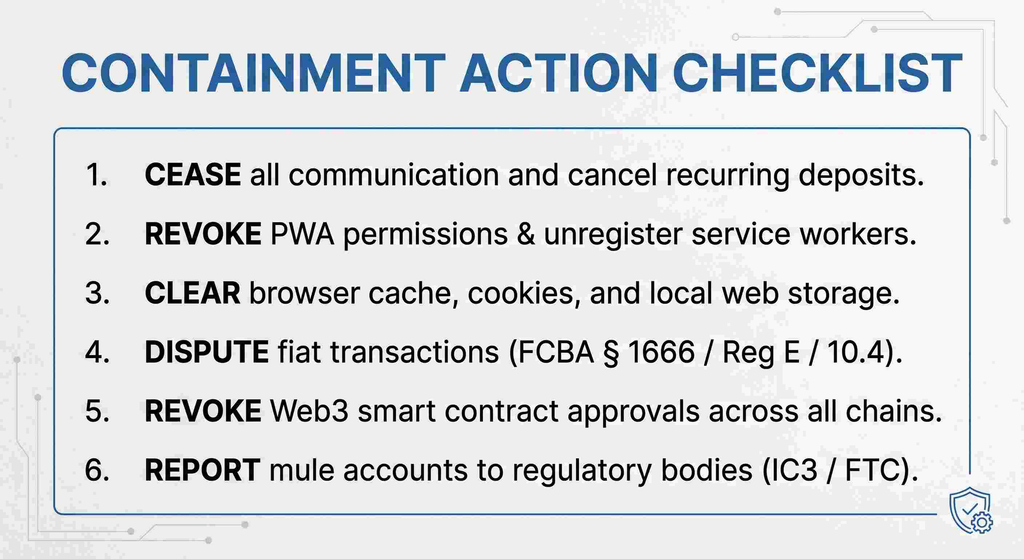
- Immediate Financial Quarantine: Terminate all communication with platform personnel. Refuse all demands for secondary verification, VIP deposits, or unfreeze fees.
- Purge PWA & Service Worker Permissions: Navigate to browser settings, select Site Settings for
Slothoku199jp.live, select Clear data & cookies, and manually unregister all active service workers located under your browser’s application management dashboard. - Revoke Local Push Notifications: Disable all background notification rights to prevent real-time delivery of malicious link redirects or phishing prompts.
- Credential Invalidation: Reset credentials, usernames, passwords, and multi-factor authentication (MFA) configurations across all personal banking, primary email, and legitimate cryptocurrency exchange accounts that shared security data with the fraudulent domain.
Call to Action
Please share this article to spread awareness. Follow us on Facebook, Twitter, and Instagram for more scam alerts. If you doubt the legitimacy of any website or investment plan, DM us on social media — we’ll help you verify.
“Scammers evolve daily. Subscribe to our scam‑alert list and stay one step ahead.”